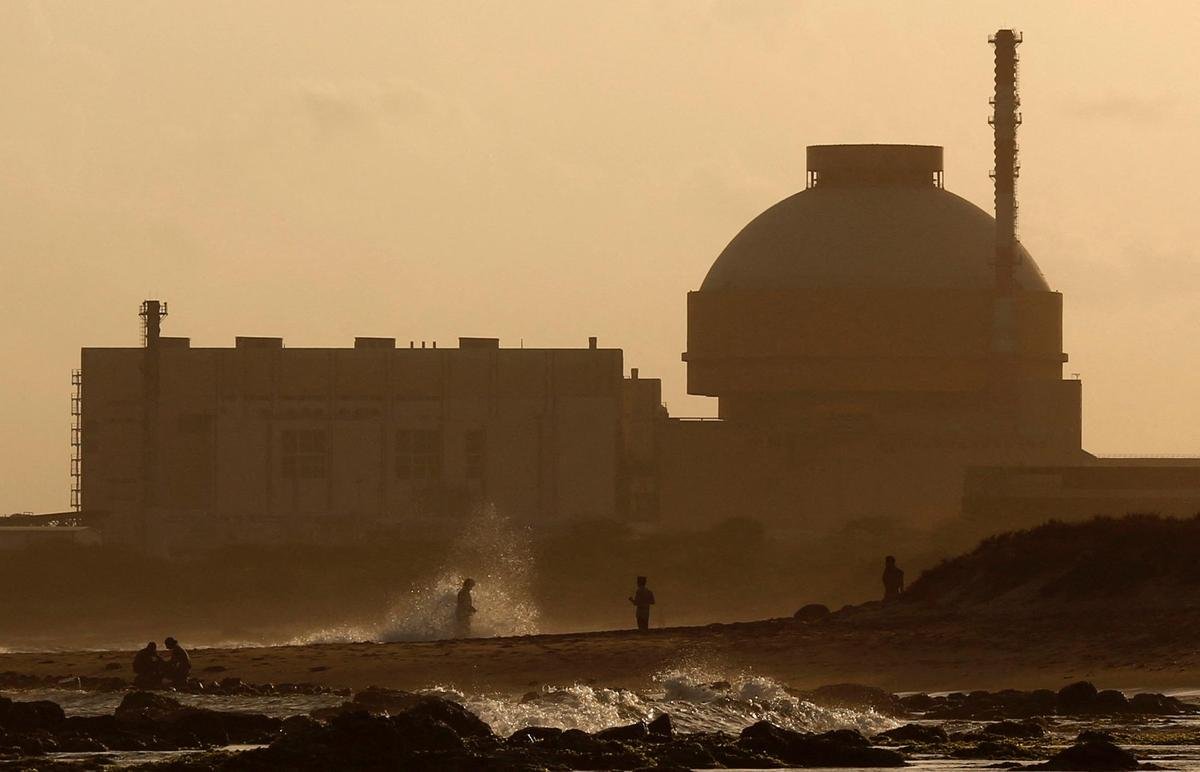
Context
In July 2026, ransomware group World Leaks published nearly 19,000 files totalling about 14.3 GB, allegedly linked to the Kudankulam Nuclear Power Project. The incident involved data held outside NPCIL’s nuclear control systems, highlighting cybersecurity risks from contractors, data centres and extended supply chains.
What the Kudankulam Incident Revealed
- Third-party exposure: Project data stored on a Yotta-hosted server used by Reliance Infrastructure was compromised, showing that sensitive information can remain vulnerable outside the plant operator’s core network.
- Reported data exposure: The published material reportedly included engineering drawings, supplier information and inspection records, creating potential reconnaissance risks even without access to reactor systems.
- Core systems unaffected: NPCIL stated that the material related to common and conventional facilities, and no public evidence shows compromise of nuclear safety or reactor-control systems.
- Recurring peripheral risk: The 2019 Dtrack malware incident also affected an Internet-connected administrative system, reinforcing the need to secure networks beyond isolated critical systems.
Supply-Chain Cybersecurity Risk
- Expanded attack surface: Critical infrastructure depends on contractors, suppliers, software providers and cloud platforms; each additional entity creates another potential point of compromise.
- Information as a security asset: Stolen technical documents can support targeted phishing, social engineering and reconnaissance, even without direct access to operational controls.
- Weakest-link problem: Core facilities may follow strict cybersecurity standards, while vendors handling related data may operate under weaker controls.
- Implication: Critical-infrastructure protection must secure the entire information lifecycle and vendor ecosystem, not only the physical facility or control network.
Cybersecurity Governance in India
- CERT-In: Under Section 70B of the Information Technology Act, 2000, CERT-In is the national agency for cyber-incident response; its 2022 directions require specified incidents, including ransomware and data breaches, to be reported within six hours.
- NCIIPC: Under Section 70A, the National Critical Information Infrastructure Protection Centre is the national nodal agency for protecting Critical Information Infrastructure.
- Coverage gap: Sensitive technical information may be stored with contractors or commercial data centres outside the infrastructure operator’s direct control, making uniform security obligations across the supply chain essential.
- Data-protection limitation: The Digital Personal Data Protection framework primarily protects personal data; non-personal engineering or operational information requires separate protection through contracts, sectoral rules and cybersecurity standards.
Strengthening Supply-Chain Security
- Uniform vendor standards: Contractors, subcontractors and cloud providers handling sensitive infrastructure information should meet mandatory security, audit and incident-reporting requirements.
- Data classification: Sensitive information should be shared on a need-to-know basis, with defined access, retention and deletion controls.
- Zero-trust architecture: Every user, device and access request should be verified, reducing the possibility of lateral movement after a breach.
- End-to-end audits: Penetration testing and red-team exercises should evaluate the entire vendor ecosystem, not merely the principal operator’s network.
- Clear accountability: Contracts and sectoral regulations should define responsibility for prevention, reporting, investigation and remediation.
Significance
- National-security value: Sensitive project information can create strategic risk even when operational systems remain uncompromised.
- Governance lesson: Critical-infrastructure protection must extend beyond the operator to contractors, cloud providers and other third parties.
- Accountability: Clear security duties and incident-reporting obligations can prevent responsibility from becoming fragmented across multiple organisations.
FAQs
Q1. What happened in the 2026 Kudankulam incident?
Nearly 19,000 project-related files were reportedly published after a breach involving a server used by Reliance Infrastructure and hosted by Yotta.
Q2. Were Kudankulam’s reactor-control systems compromised?
There is no public evidence that nuclear safety or reactor-control systems were compromised.
Q3. What is supply-chain cybersecurity?
It protects systems and information handled by vendors, contractors, cloud providers and other third parties.
Q4. What is the difference between CERT-In and NCIIPC?
CERT-In handles cyber-incident response, while NCIIPC focuses on protection of Critical Information Infrastructure.
Q5. What is the main lesson from the incident?
Critical infrastructure remains vulnerable if sensitive information outside the core facility is inadequately protected.